CV GDPR: What Recruitment Agencies Need to Get Right With Candidate CVs
How UK GDPR applies to candidate CVs in a recruitment agency: lawful basis, data minimisation in client submissions, retention, and the questions to ask any CV formatting tool that processes candidate data.
A candidate CV is one of the densest pieces of personal data an agency handles. Name, contact details, employment history, education, sometimes health information or a photograph — supplied by someone who wants a job, and forwarded to third parties as a matter of routine. UK GDPR applies to all of it. This is a practical guide to the parts that actually affect a recruitment workflow, including the questions worth asking any tool that touches candidate CVs. It is general information rather than legal advice; take advice on your specific circumstances.
A CV is personal data, and sometimes more than that
Everything on a CV that identifies a living person is personal data. That much is uncontroversial. What agencies underestimate is how often CVs carry special category data, which attracts stricter conditions.
A photograph can reveal ethnicity. A gap explained as 'medical leave' is health data. Trade union roles, religious institutions in an education history, or volunteering for a political organisation all fall into special categories. None of it was requested; candidates simply include it.
The practical implication is not to refuse such CVs. It is that forwarding them onward without thought is a bigger decision than it feels, and that removing what a client does not need is both good practice and good compliance.
Lawful basis: usually legitimate interests, and it needs writing down
Most recruitment agencies rely on legitimate interests for processing candidate data, rather than consent. That is generally the more robust choice: consent must be freely given and withdrawable, and a candidate who withdraws consent mid-process leaves you unable to do the job they asked you to do.
Legitimate interests is not a free pass. It requires a balancing assessment you can produce: your interest in placing the candidate, whether the processing is necessary for it, and whether it overrides the individual's rights. Write it down once, review it when your workflow changes.
Special category data needs a separate condition on top. Many agencies handle this by not processing it at all — removing it rather than justifying it.
Data minimisation is the principle that bites in client submissions
Minimisation says you process what is adequate, relevant and limited to what is necessary. Applied to a client submission, that is a sharper question than it first appears: does this client, at this stage, need the candidate's home address, date of birth, full contact details and photograph in order to decide whether to interview them?
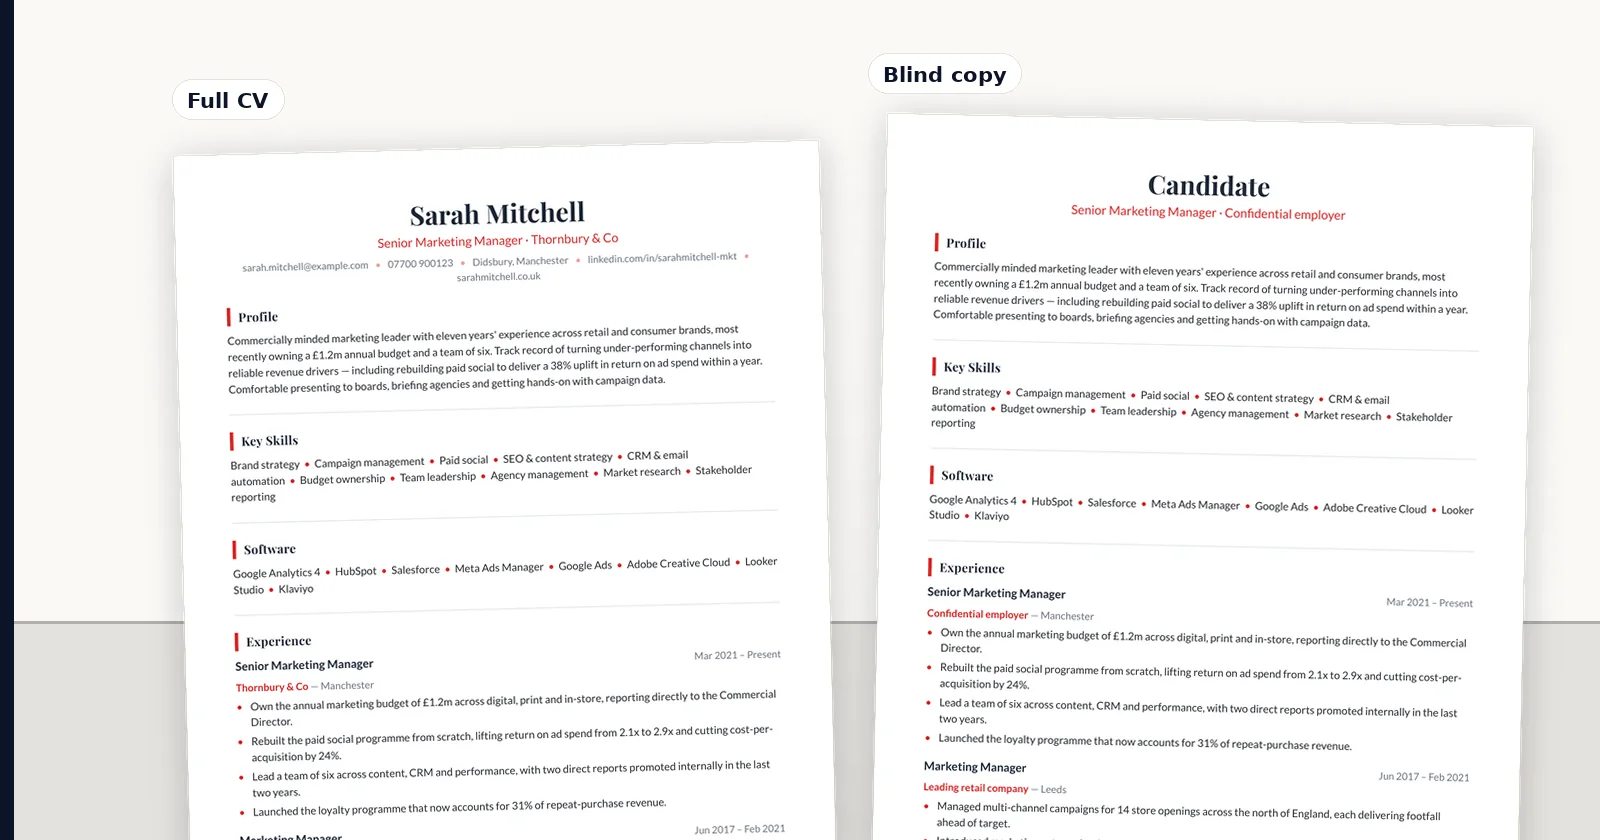
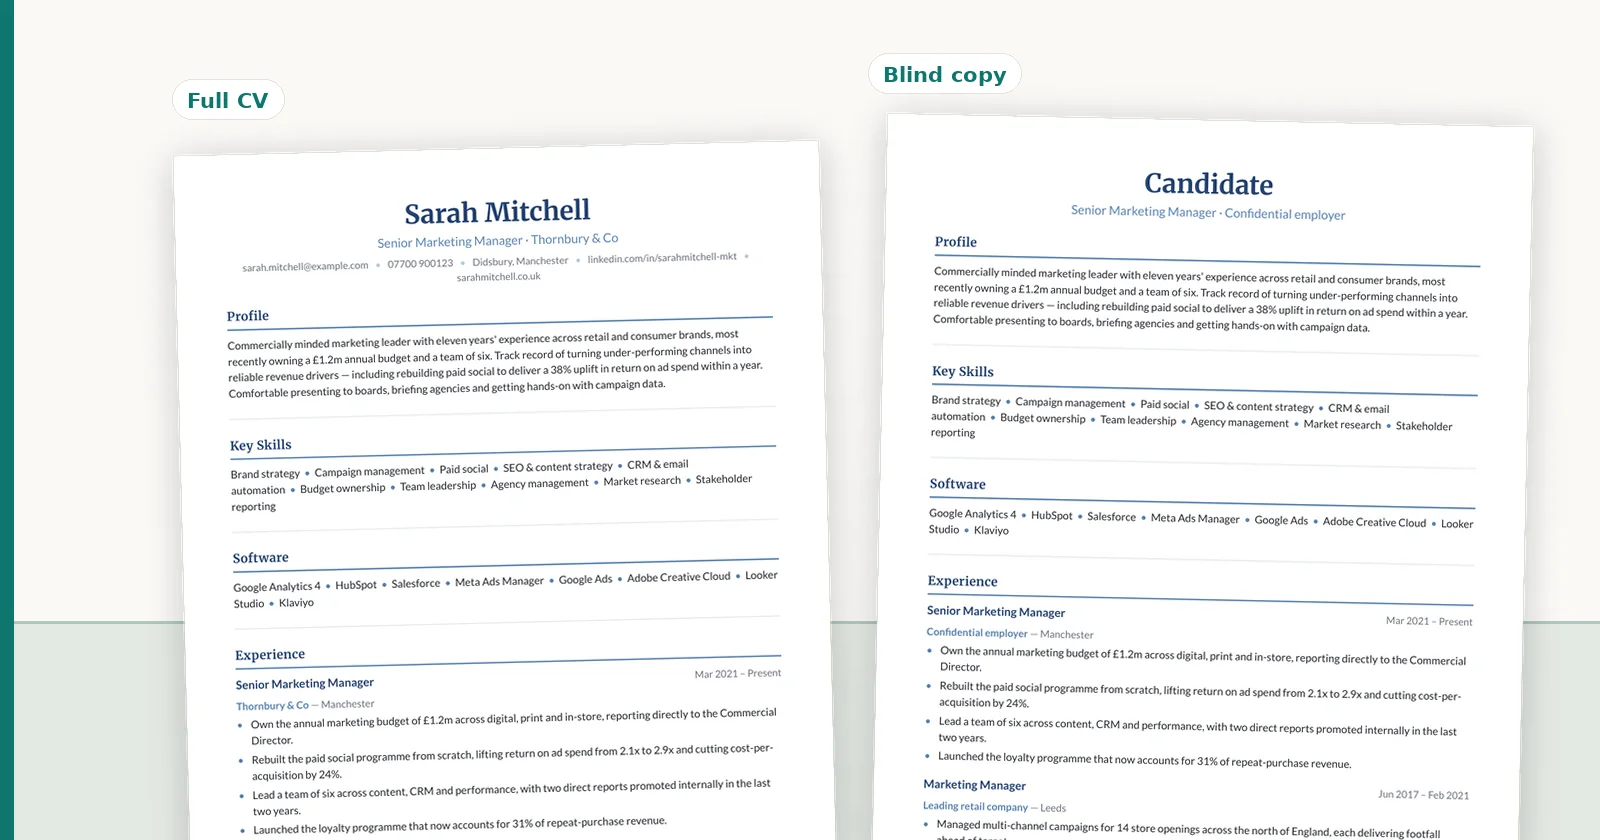
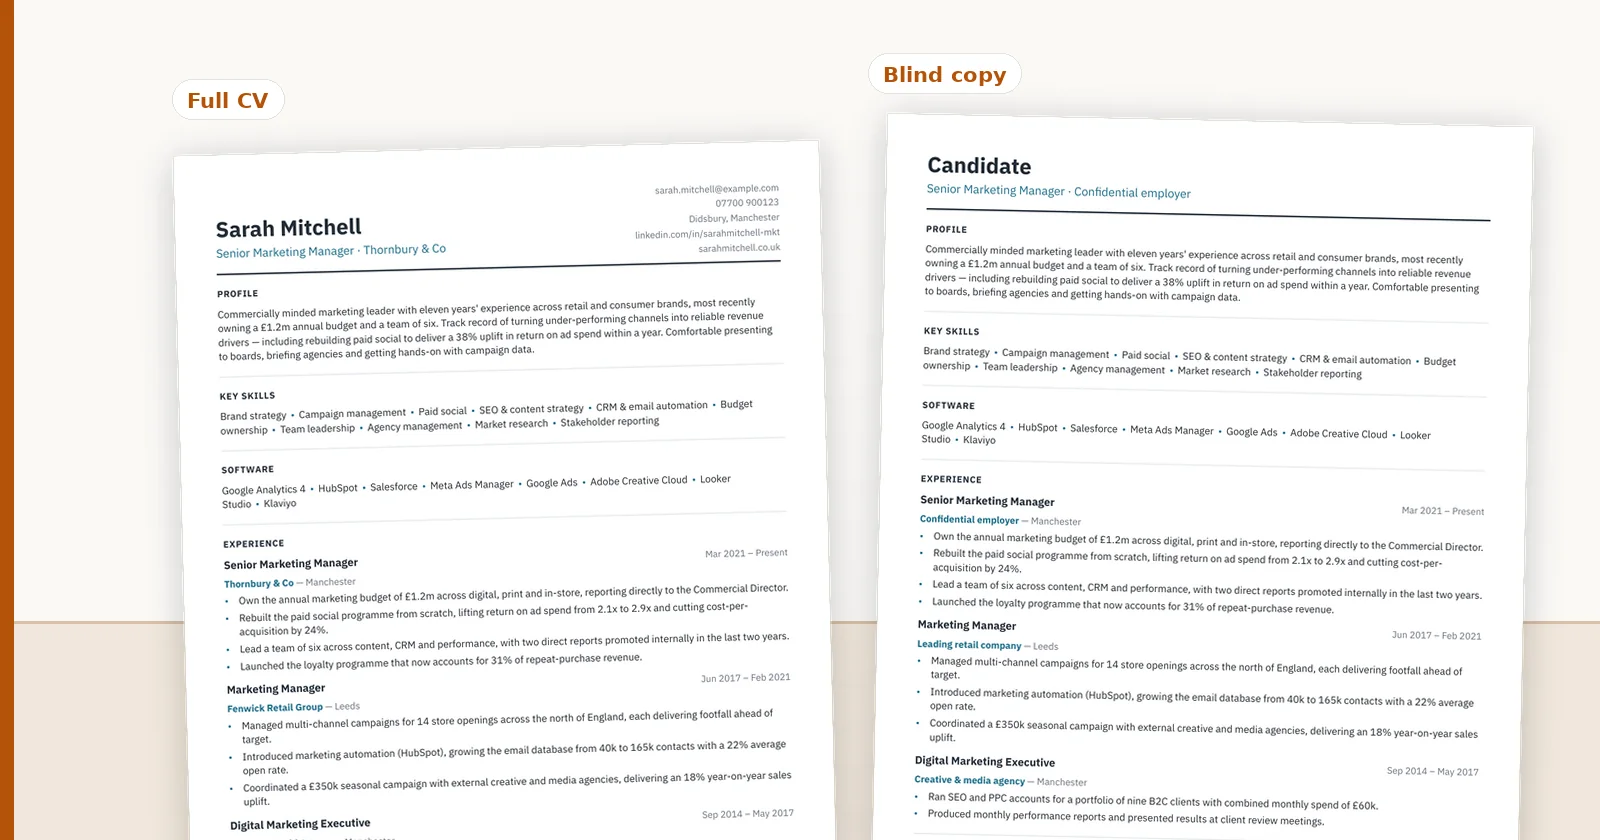
Almost always, no. At first submission a client needs to assess capability. Contact details exist so they can contact the candidate — through you. That is exactly why blind and partially redacted submissions are good practice, not merely a fair-hiring gesture.
This is the clearest overlap between compliance and doing the job well. Sending less is both more defensible and, as blind-hiring research consistently shows, often produces better first-stage decisions.
- Remove home address and full contact details from first-stage submissions
- Remove date of birth, and graduation years if they act as a proxy for it
- Remove photographs unless the client has a genuine, stated need
- Strip health information, and anything else that fell into a special category unasked
- Keep the identified version on file — you need it when an interview is arranged
Transparency: what candidates must be told
Candidates have to know what happens to their CV. In practice that means a privacy notice they can actually reach, saying who you are, what you do with their data, the lawful basis, who you share it with, how long you keep it, and their rights.
The share-with element is the one agencies handle loosely. 'We may share your CV with our clients' is thin if you have not told the candidate before sending it to a specific employer. Many agencies confirm each submission with the candidate anyway, for commercial reasons — it also happens to be the transparent position.
If you use AI to reformat or rewrite CVs, that is processing too, and it usually means sending the content to a third-party model provider. Candidates should be able to find that out from your notice.
Do candidates need a GDPR statement on their CV?
Candidates often ask whether to add a GDPR statement or consent clause to their CV, and agencies receive plenty that carry one ("I consent to the processing of my personal data for recruitment purposes"). In the UK it is not required and changes little.
The clause is a habit imported from Poland and parts of continental Europe, where employers have historically asked for it. Under UK GDPR, an agency processing a CV for recruitment normally relies on legitimate interests, and its obligations come from that basis and its privacy notice, not from a sentence the candidate typed. A consent clause on the CV does not replace the agency telling the candidate how their data will be used, and it does not oblige the agency to treat the processing as consent-based.
The practical position: leave the statement on if a candidate has included it, do not add one to the formatted CV, and make sure your own privacy notice and submission confirmations do the real work. Jobs in Poland and some other EU countries are the exception, where employers may still expect the clause.
Retention: the requirement most agencies quietly fail
You may not keep candidate data indefinitely because it might be useful one day. You need a defined retention period, a reason for it, and a mechanism that actually deletes.
There is no statutory number. Many UK agencies land on two years from last meaningful contact, on the basis that a candidate's CV is stale beyond that and the relationship has lapsed. What matters is that the period is deliberate and applied, rather than a policy document describing a deletion that never happens.
The uncomfortable question worth asking internally: if a candidate exercised their right to erasure today, could you find every copy? The branded submissions on a shared drive, the versions in email, the exports on a consultant's laptop. Workflows that generate a new branded file per submission make that question much harder to answer than workflows that render from a single stored record.
Your CV tool is a processor — and you are responsible for it
When you use software to format candidate CVs, you remain the controller and the vendor is your processor. Article 28 requires a written contract governing that relationship, and the obligation to check they are suitable sits with you, not them.
This is where most diligence stops at 'they say they are GDPR compliant', which is not a meaningful statement. The questions below are answerable and revealing.
- Do you offer a data processing agreement, and what does it actually commit you to?
- Where is candidate data stored, and in which jurisdiction?
- If AI is used, which model provider receives the CV content, and is it used to train their models?
- Are transfers outside the UK or EEA covered by appropriate safeguards?
- How long do you retain uploaded files and generated exports, and can I configure it?
- Can I delete a candidate's data completely, including generated outputs and any share links?
- Who inside your organisation can access candidate files, and is that access logged?
- How do you separate one agency's data from another's?
A workable position
None of this requires a compliance department. It requires a handful of decisions made deliberately and then applied consistently.
Write down your lawful basis. Minimise what goes to clients at first stage. Publish a privacy notice that describes what actually happens, including AI processing. Set a retention period and make deletion real. Get a DPA from every processor and ask them the questions above. Put expiry on share links.
Do that and you are ahead of most of the market — and, not coincidentally, sending better submissions.
FAQ
Q01Do we need candidate consent to send a CV to a client?
Most agencies rely on legitimate interests rather than consent, which is generally more robust because consent can be withdrawn mid-process. You still need a documented balancing assessment, a privacy notice explaining that CVs are shared with clients, and in practice most agencies confirm specific submissions with the candidate anyway.
Q02How long can a recruitment agency keep a candidate's CV?
There is no statutory period. You need a defined, justifiable retention period and a mechanism that actually deletes — many UK agencies use two years from last meaningful contact. The harder question is whether you could locate every copy, including branded exports and share links, if erasure were requested.
Q03Is using AI to rewrite a CV a GDPR issue?
It is processing, and it usually means sending candidate data to a third-party model provider, so it belongs in your privacy notice and your processor diligence. Ask which provider receives the content and whether it is used for training. Formatting is not automated decision-making under Article 22, because no decision about the person is being made by the system.
Q04Should we remove contact details before sending a CV to a client?
Usually yes at first submission. Data minimisation asks what the client needs to decide whether to interview, and that is capability rather than a home address or date of birth. It also protects the relationship, since the client contacts the candidate through you.
Q05What should we ask a CV formatting vendor about data protection?
Whether they provide a DPA, where data is stored, which AI provider receives CV content and whether it trains on it, what safeguards cover international transfers, how long files and exports are retained, whether you can delete completely, and how one agency's data is separated from another's. 'We are GDPR compliant' on its own tells you nothing.
Q06Is a CV protected under GDPR?
Yes. A CV identifies a living person, so it is personal data under UK GDPR, and parts of it (health information, a photograph, trade union roles) can be special category data. Anyone processing it, agencies and their software suppliers included, needs a lawful basis, a stated retention period and appropriate security.
Q07What does GDPR mean on a CV?
Usually a consent clause the candidate has added, saying they agree to their data being processed for recruitment. It is common in Poland and parts of Europe. In the UK it is not required: agencies normally rely on legitimate interests and must explain their processing in a privacy notice regardless of what the CV says.
ConnectIQ Editorial documents practical recruitment operations and the controls implemented in the ConnectIQ product. This guide is general operational information, not legal advice.